
Table of Contents
ToggleThe world’s biggest cryptocurrency exchange Binance has confirmed theft of assets worth more than $6.3 billion in a cyberattack that took place on October 30, 2026, and is set to become one of the biggest cybersecurity events in the cryptocurrency sector.
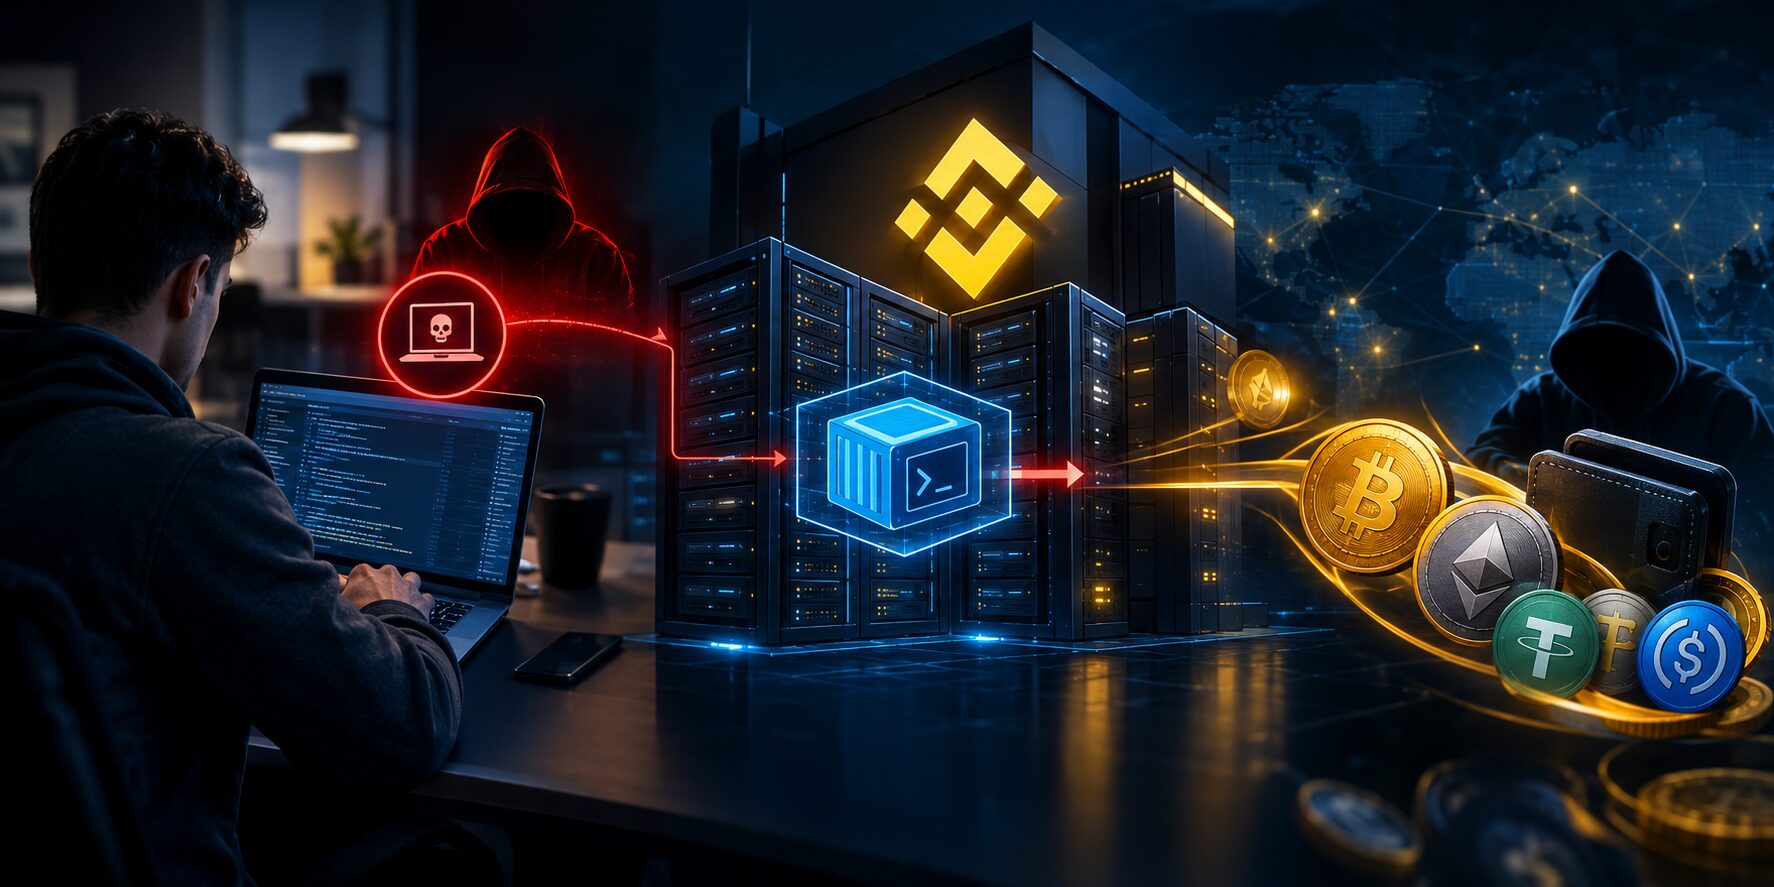
As per the initial investigation carried out by Binance, it appears that hackers got a hold of the laptop of a DevOps engineer and gained access to internal networks for fraudulent withdrawal of cryptos.
The platform is working with blockchain companies to freeze nearly $3 billion in stolen assets as the investigation is still ongoing.
In brief, How the Attack Was Done?
Binance believes the attack happened due to a compromised laptop of a DevOps engineer.
The suspected hacker has used this access to get into the service container within the Binance infrastructure and make unauthorized withdraws.
DevOps engineers are involved in the management of the development and operational environment, thus becoming the primary target for cybercriminals by their end-points.
Binance has not mentioned how the Compromised laptop was first hacked or what security measures were violated.
Impact on Finances and Asset Freezing
It is believed by Binance that around $6.3 billion worth of cryptocurrency assets were affected due to the incident.
In response to the situation, along with other cryptocurrency issuers, Binance was able to freeze approximately $3 billion on the chain.
Tether and Circle also took part in the measures.
The total amount of stolen or recovered assets is still unclear.
Additionally, this incident raises issues of security of the centralized exchanges among the users of cryptocurrency market.
Binance Responds to the Security Breach
Following the discovery, Binance temporarily suspended cryptocurrency deposits and withdrawals while conducting additional security checks.
The exchange revoked affected address authorizations and began coordinating with law enforcement agencies and blockchain intelligence partners to trace suspicious transactions.
Binance assured customers that their funds remain safe and committed to covering confirmed losses through its Secure Asset Fund for Users (SAFU) and company reserves.
The company also announced plans to release a detailed technical post-incident report and updated Proof of Reserves once remediation is completed.
What Implications Does This Case Hold for Cybersecurity?
The alleged assault suggests that hacking a single privileged worker endpoint can endanger the critical financial system.
Companies with sensitive resources have no choice but to beef up endpoint protection, implement least-access policies, secure admin credentials and vigilantly monitor privileged events.
Implementing stringent rules for service containers and extra authorizing procedures for valuable transactions can also ameliorate damage caused by hacked accounts.
The incident at Binance teaches us an important lesson in cybersecurity — securing critical infrastructure requires not just protection of servers and applications but of employees and devices that can access them.
Let’s refine your stalking skills; go through our Instagram and LinkedIn.