
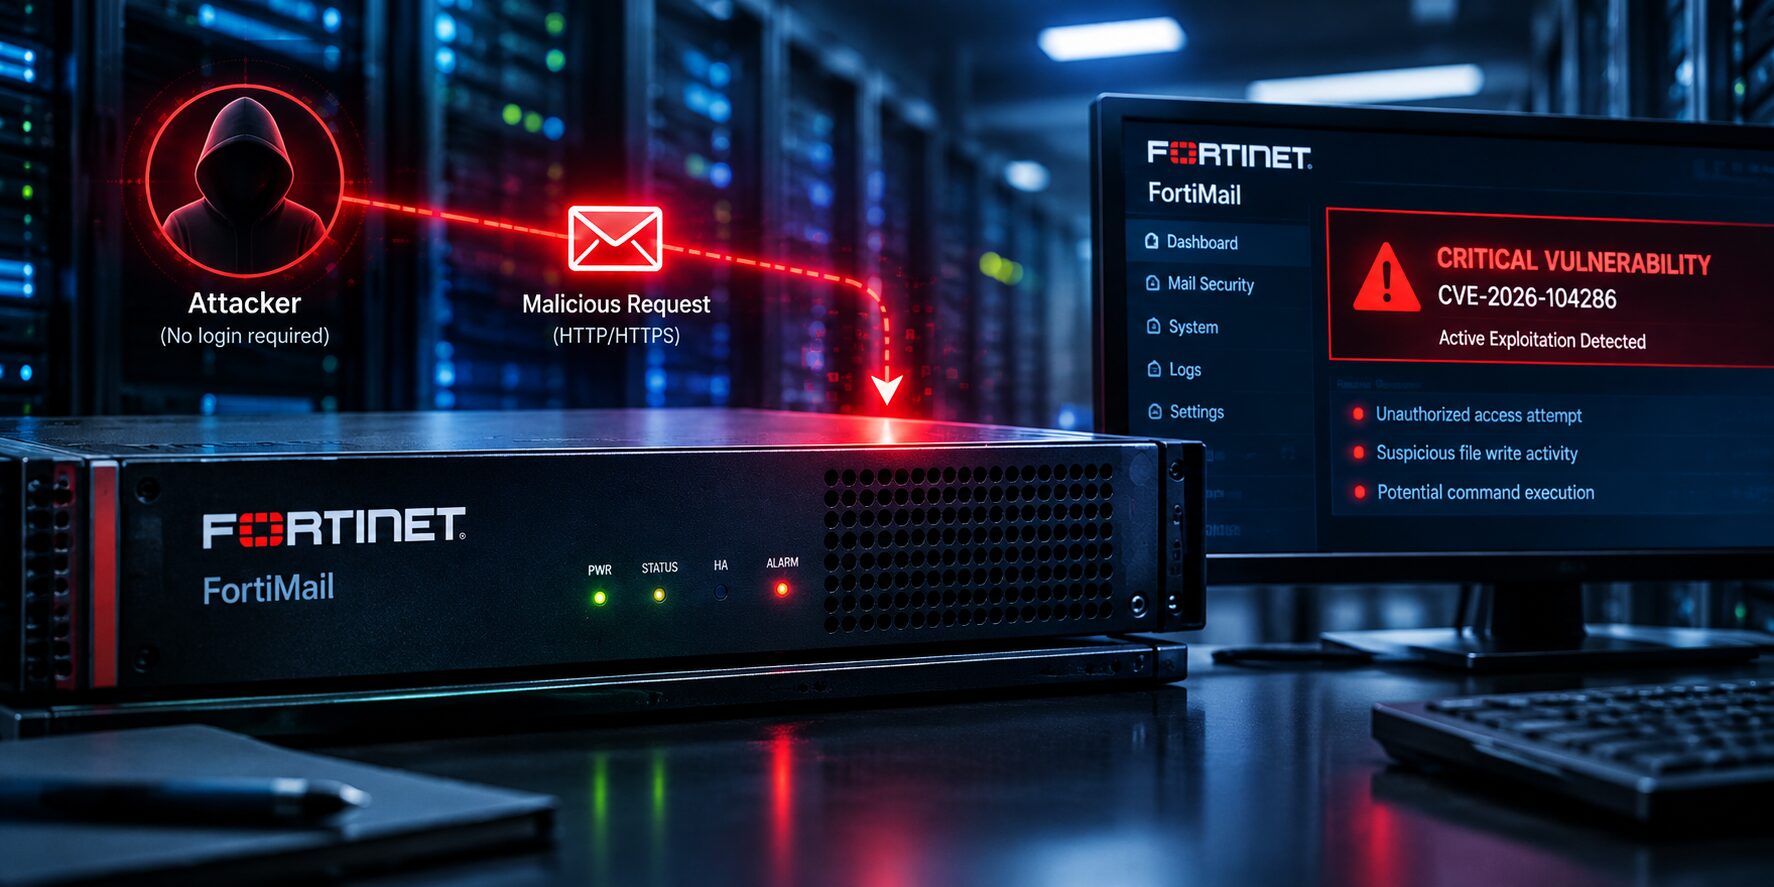
Fortinet has sounded alarm on a flaw in FortiMail. It is reported that attackers are utilizing it in real life situations.
This flaw is identified as CVE-2026-104286 and given the 9.8 severity score in CVSS. The vulnerability lies in the FortiMail management interface and concerns path traversing with incorrect processing of NULL characters.
An interesting thing, the vulnerability doesn’t require a log-in. An attacker needs to send some special HTTP/HTTPS request to the vulnerable system and write files, thus launching unauthorized commands.
The versions of FortiMail that need to be updated are the following – FortiMail 8.0.0 – 8.0.1, 7.6.0 – 7.6.6, 7.4.0 – 7.4.8 and 7.2.0 – 7.2.9.
If you are on 7.2 version you need to upgrade to 7.4 or above. The updates on the rest versions will be released in 7.4.9, 7.6.7, and 8.0.2, but these versions haven’t been released yet.
If you are unable to patch your systems immediately, you should minimize your risk exposure. One suggestion from Fortinet is to disable IBE capabilities whenever applicable. Also, verify that there is no direct reach to the management interface from the public internet. Limiting access for administrators to trustworthy internal networks is essential.
Fortinet has compiled indicators of compromise to make it easier for teams to assess their systems. These consist of strange files, changed components, unexpected log activity, and addresses involved in the attacks. In some cases, compromised systems have been observed sending archived data to an adversary’s infrastructural resources.
CISA has included the vulnerability in its database of Known Exploited Vulnerabilities implying that it is being exploited.
If you are using FortiMail, check your version, inspect your systems for signs of compromise and take advantage of Fortinet’s suggestions as well as apply the patch when available.